

Chapter 1
Starting Your BCM Implementation for the Malaysian Communications and Multimedia Commission
Introduction

This eBook, Starting Your BCM Implementation for the Malaysian Communications and Multimedia Commission, is the third publication in the three-part eBook series:
Managing Business Continuity Management for the Malaysian Communications and Multimedia Commission (MCMC): A Practical Guide to Organisational Resilience, Service Continuity, and Regulatory Excellence
The three eBooks are designed to work together:
- Understanding Your Organisation for the Malaysian Communications and Multimedia Commission
- Implementing Business Continuity Management for the Malaysian Communications and Multimedia Commission
- Starting Your BCM Implementation for the Malaysian Communications and Multimedia Commission
eBook 1 and eBook 2 provide the pre-reading, contextual understanding, methodology, and implementation guidance needed before the organisation begins completing the detailed BCM templates. This third eBook moves from understanding and preparation into hands-on implementation.
Its purpose is to help MCMC prepare, update, or strengthen the working documentation required for a Business Continuity Management project using a structured BCM planning methodology aligned, where applicable, with the principles of ISO 22301.
The emphasis in this eBook is practical. It is not intended merely to explain BCM concepts. Instead, it provides a structured implementation pathway through the major analytical and planning phases of a BCM project and shows how the outputs from each phase connect to the next.
The implementation sequence is:
Risk Analysis and Review
→ Business Impact Analysis
→ Business Continuity Strategy
→ Business Continuity Plan Development
Each phase produces specific outputs that should be reviewed, validated, and approved by the appropriate business, technical, and management stakeholders.
Purpose of this eBook

The primary purpose of this eBook is to provide MCMC with a practical implementation reference for preparing or updating the documentation required during a BCM project.
It is intended to support organisations that are either:
- implementing BCM for the first time;
- formalising an existing BCM programme;
- updating an established programme;
- aligning existing documentation with ISO 22301;
- strengthening recovery strategies and continuity plans;
- improving consistency across Critical Business Functions; or
- preparing business units to participate more effectively in BCM workshops and exercises.
Unlike an introductory BCM publication, this eBook drills down into the specific worksheets, templates, analyses, and planning outputs required during implementation.
The central implementation logic is:
Understand the Organisation
→ Identify Threats
→ Determine What Is Critical
→ Assess Impact Over Time
→ Establish Recovery Requirements
→ Select Recovery Strategies
→ Determine Minimum Resources
→ Develop Business Continuity Procedures
→ Exercise and Improve
The result should be a set of traceable BCM documents in which the rationale for each recovery requirement can be linked back to an identified business need.
Relationship with eBooks 1 and 2
This eBook should be read together with the first two publications in the series.
eBook 1: Understanding Your Organisation for MCMC
The first eBook establishes the organisational context required before detailed BCM analysis begins.
It helps establish an understanding of:
- MCMC's organisational and operating environment;
- its regulatory responsibilities;
- key products and services;
- organisational objectives;
- stakeholders;
- business functions;
- resources and dependencies;
- operating assumptions; and
- proposed Critical Business Functions.
This context is essential because BCM should not begin with systems or recovery facilities. It should begin with an understanding of what the organisation must continue to achieve during disruption.
eBook 2: Implementing Business Continuity Management for MCMC
The second eBook establishes the BCM implementation approach and explains how the programme should be organised, governed, and executed.
It provides the methodology needed to move from organisational understanding into structured BCM analysis and planning.
eBook 3: Starting Your BCM Implementation for MCMC
This third eBook is the working implementation guide.
It takes the organisation into the detailed completion of:
RAR → BIA → BCS → PD
The first two eBooks, therefore, answer:
What should MCMC understand, and how should the BCM project be organised?
The third eBook answers:
What must MCMC now analyse, document, decide, and develop?
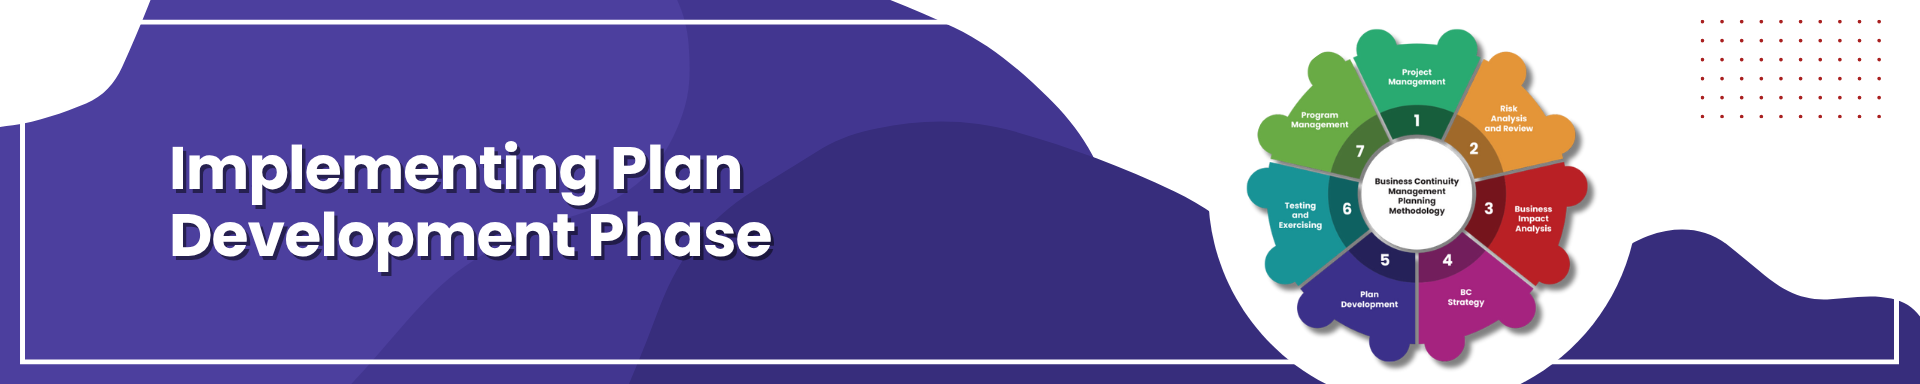
The Four Phases of the BCM Planning Methodology
The BCM implementation covered in this eBook follows four principal phases:
Phase 1 — Risk Analysis and Review
The Risk Analysis and Review phase examines threats capable of disrupting MCMC and the controls available to manage those threats.
It provides an understanding of the organisation's disruption exposure before recovery requirements and continuity strategies are finalised.
Phase 2 — Business Impact Analysis
The BIA determines which activities are critical, the consequences of their disruption, how quickly they must be recovered, and the resources and dependencies needed to support them.
This phase establishes the business requirements that should subsequently drive continuity and technology recovery decisions.
Phase 3 — Business Continuity Strategy
The BCS phase converts the BIA requirements and risk findings into practical solutions for reducing disruption exposure and recovering affected activities.
It determines how MCMC intends to continue priority regulatory activities when normal resources are unavailable.
Phase 4 — Business Continuity Plan Development
Plan Development translates approved recovery strategies into actionable procedures.
It answers:
Who does what, when, where, using which resources, and through which escalation and communication arrangements when disruption actually occurs?

Risk Analysis and Review (RAR)
The Risk Analysis and Review phase begins by identifying credible threats and evaluating the organisation's exposure to them.
Three principal templates are completed.
RAR T1 — List of Threats
The first template identifies the specific threats capable of disrupting MCMC.
Threats may arise from areas such as:
- natural hazards;
- denial of access;
- workforce disruption;
- supply-chain failure;
- technology failure;
- cyber incidents;
- telecommunications disruption;
- utility failure; and
- physical security events.
The objective is to establish a sufficiently comprehensive threat register before attempting to determine which risks warrant further treatment.
RAR T2 — Treatment and Control
The second template examines how the identified threats are presently managed.
It considers:
- risk avoidance;
- risk reduction;
- risk transference;
- risk acceptance;
- existing controls; and
- additional controls required.
A control should not be regarded as effective merely because it exists. Its ownership, reliability, maintenance, testing, and actual effectiveness should also be considered.
RAR T3 — Risk Impact and Likelihood Assessment
The third template evaluates the consequences and likelihood of each threat after considering existing controls.
The assessment normally considers impacts across several dimensions, including:
- finance;
- operations;
- legal and regulatory obligations;
- reputation;
- public or social consequences;
- people; and
- assets, technology, and information.
The relationship can be represented as:
Threat
→ Existing Controls
→ Current Exposure
→ Impact
→ Likelihood
→ Risk Rating
→ Mitigation Priority
The output helps determine where additional mitigation, recovery planning or management attention is required.
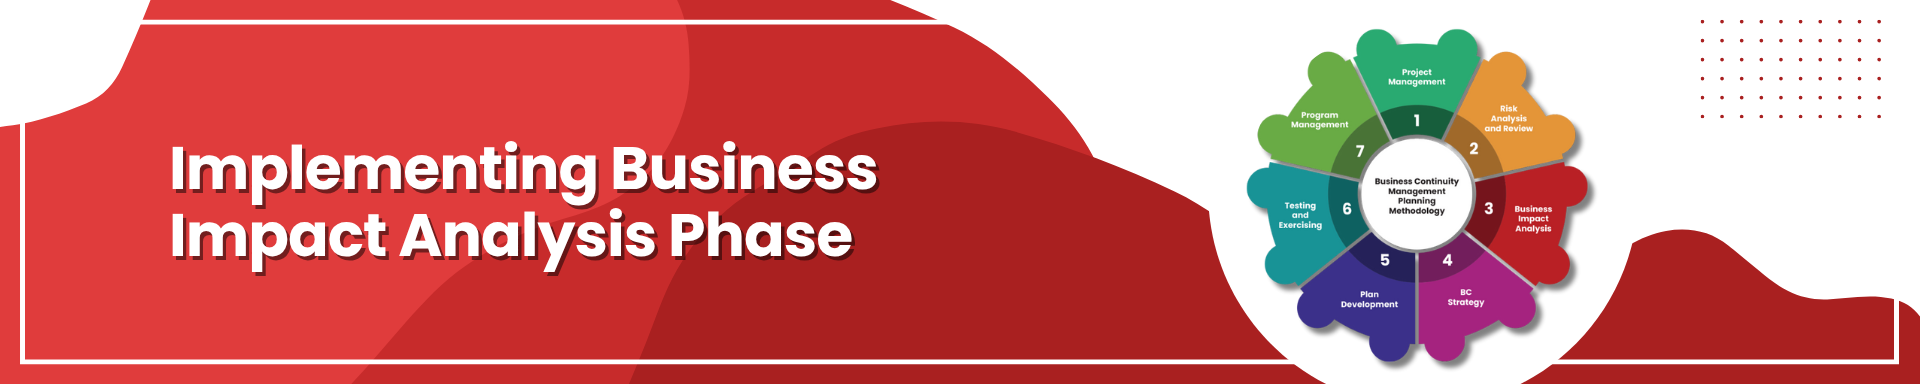
Business Impact Analysis (BIA)
The Business Impact Analysis is the central analytical phase of BCM.
The BIA should not begin by asking which systems should be recovered first. Instead, it should determine:
Which business functions must continue or recover first, and what do those functions require to operate?
For each Critical Business Function, MCMC should complete the following seven components.
Part 0 — Corporate MBCO and Products and Services
This establishes the broader organisational continuity requirement.
The Corporate Minimum Business Continuity Objective (MBCO) defines the minimum level of products, services, or organisational capability that should be maintained during significant disruption.
It provides top-down direction before business units determine their individual recovery requirements.
Part 1 — Identification of Business Functions
Each Critical Business Function is decomposed into the business activities or Sub-Critical Business Functions that support it.
For each activity, the analysis should establish the minimum level that must be maintained during disruption.
This creates the connection:
Corporate MBCO
→ Critical Business Function
→ Sub-Critical Business Function
→ BU MBCO
Part 2 — Impact Areas of Business Functions
This component assesses the consequences of disruption to each business activity across relevant impact dimensions.
It establishes why the activity matters and what consequences arise when it cannot be performed.
Part 3 — Impact Over Time of Business Functions
This component assesses how disruption consequences escalate with time.
It supports the determination of:
- Maximum Tolerable Period of Disruption;
- Recovery Time Objective
- recovery priority; and
- minimum continuity requirements.
The principle is:
Longer Disruption → Increasing Consequences → Unacceptable Impact
The RTO should normally fall before the MTPD.
Part 4 — Supporting IT Systems and Applications
Once the Business RTO has been established, the organisation can determine which systems and applications are required to support recovery.
The correct sequence is:
Business Requirement
→ Business RTO
→ Required Application
→ System RTO
→ Data Requirement
→ RPO
This ensures technology recovery priorities are driven by business need rather than by technical preference.
Part 5 — Inter-dependencies
This identifies the internal and external relationships upon which recovery depends.
Examples include:
- other business units;
- management;
- suppliers;
- government agencies;
- communications providers;
- technology services;
- specialist personnel; and
- external partners.
The key question is:
What else must be available before this business function can recover successfully?
Part 6 — Vital Records
The final BIA component identifies the minimum information and records required to continue the business activity and demonstrate regulatory accountability.
Vital records may include:
- case records;
- regulatory decisions;
- evidence;
- correspondence;
- approvals;
- contact directories;
- incident information;
- action registers; and
- statutory or regulatory documents.
The objective is not to classify every organisational document as vital. It is to identify the information without which the Critical Business Function cannot operate or demonstrate accountability.
Critical Business Functions for MCMC
The proposed Critical Business Functions represent the principal regulatory and supporting outcomes that should be subjected to a detailed BIA.
The list marks the beginning of the BIA phase and should be inserted into the working BCM report for management validation.
|
CBF Code |
Critical Business Function |
|
CBF-1 |
Communications and Multimedia Regulatory Oversight |
|
CBF-2 |
Spectrum Management and Radiofrequency Coordination |
|
CBF-3 |
Licensing and Regulatory Authorisation Services |
|
CBF-4 |
Consumer Complaint and Protection Services |
|
CBF-5 |
Communications Sector Incident Monitoring and Coordination |
|
CBF-6 |
Regulatory Compliance Monitoring and Enforcement |
|
CBF-7 |
Critical Regulatory Information and Data Services |
|
CBF-8 |
Critical Digital Regulatory Platforms and Online Services |
|
CBF-9 |
Stakeholder, Government, and Crisis Communications |
|
CBF-10 |
Critical ICT and Cybersecurity Services |
|
CBF-11 |
Communications Infrastructure Regulatory Coordination |
|
CBF-12 |
Postal and Courier Regulatory Oversight |
The term Critical Business Function should not be interpreted as meaning that every component of the function requires an identical recovery priority.
Each CBF should subsequently be decomposed into its Sub-Critical Business Functions and assessed individually.
The correct progression is:
Organisational Mandate
→ Products and Services
→ Critical Business Functions
→ Sub-Critical Business Functions
→ Impact Analysis
→ Recovery Requirements
This prevents recovery priorities from being assigned only at the department or system level.
The list above should also be regarded as subject to organisational validation. MCMC's management and relevant business owners should confirm that the proposed CBFs accurately represent those functions whose disruption could materially affect statutory, regulatory, public-interest, or operational outcomes.

Business Continuity Strategy (BCS)
Once the Risk Assessment and BIA have established what threatens the organisation and what must be recovered, the Business Continuity Strategy phase determines how continuity will be achieved.
Three principal templates are developed.
BCS T1 — Mitigation Strategies
Mitigation addresses risks and control weaknesses identified through the RAR.
Typical strategies may include:
- reducing single points of failure;
- strengthening facility protection;
- improving cyber controls;
- increasing redundancy;
- diversifying suppliers;
- improving workforce succession;
- strengthening backup and recovery;
- improving communications resilience; and
- increasing monitoring and early warning.
The purpose is to reduce the probability or consequences of disruption before it becomes necessary to invoke full recovery arrangements.
BCS T2 — Recovery Strategies and Justifications
Recovery strategies determine how each critical activity will resume within its required RTO.
Potential strategies include:
- remote working;
- alternate offices;
- manual workarounds;
- cross-trained personnel;
- workload prioritisation;
- high-availability technology;
- disaster recovery environments;
- cloud recovery;
- reciprocal arrangements; and
- third-party recovery services.
The strategy selected should be justified according to the BIA requirement.
The decision logic is:
Business RTO
- BU MBCO
- Dependencies
- Risk Exposure
- Cost
- Reliability
= Selected Recovery Strategy
BCS T3 — Minimum Resources Required During a Disaster
A recovery strategy is incomplete unless the resources required to implement it are identified.
For each Sub-Critical Business Function, the organisation should determine the minimum resources needed during disruption, including:
- personnel;
- workspace;
- laptops and equipment;
- telecommunications;
- systems and applications;
- data and records;
- specialist expertise;
- suppliers;
- approvals;
- transport; and
- other operational resources.
The important distinction is between:
Normal Operating Resources
and
Minimum Resources Required to Achieve the BU MBCO
The continuity requirement is not necessarily to recreate the full normal operating environment immediately.
Plan Development (PD)
Once the Business Continuity Strategies have been selected, they must be converted into executable procedures.
This is the purpose of the Plan Development phase.
Detailed Business Continuity Plan procedures should be developed around the specific business processes supporting each Critical Business Function.
The plans should provide sufficient instruction to enable designated personnel to respond when normal operating arrangements are unavailable.
Typical procedural areas include:
Activation
→ Initial Assessment
→ Escalation
→ Staff Notification
→ Recovery Team Mobilisation
→ Alternate Working
→ Manual Workaround
→ Technology Recovery
→ Stakeholder Communications
→ Priority Processing
→ Backlog Management
→ Return to Normal Operations
→ Post-Incident Review
The procedures should be sufficiently specific to support action but flexible enough to accommodate different disruption scenarios.
A Business Continuity Plan should not become a lengthy description of BCM theory. Its primary value is operational:
Can the designated team use the plan to restore the required business capability within the approved RTO?
Maintaining Traceability Across the Four Phases
One of the most important objectives of this eBook is to maintain traceability across the entire BCM planning process.
For example:
Risk Assessment identifies:
Telecommunications Failure.
BIA identifies:
Regulatory Incident Situation Monitoring requires recovery within one hour.
BIA dependency analysis identifies:
Telecommunications and secure communications are essential resources.
BCS determines:
Diverse communications and alternative channels are required.
Plan Development defines:
How personnel activate the alternate communication method when the primary service fails.
The full traceability chain is therefore:
Threat
→ Critical Business Function
→ Business Impact
→ MTPD
→ RTO
→ BU MBCO
→ Dependencies
→ Recovery Strategy
→ Minimum Resources
→ BCP Procedure
→ Exercise
→ Improvement
This traceability is fundamental because it allows management, auditors and BCM practitioners to understand why each continuity strategy and recovery requirement exists.
The eBook as a Compilation of BCM Project Outputs
This third eBook is intended to operate not only as guidance but also as a structured compilation of BCM project submissions.
During implementation, the organisation progressively completes and validates the templates associated with:
- Risk Analysis and Review;
- Business Impact Analysis;
- Business Continuity Strategy; and
- Business Continuity Plan Development.
The result is a working implementation record showing how the BCM programme has progressed from analysis into recovery planning.
It may therefore be used to support:
- workshop preparation;
- business-unit submissions;
- management review;
- BCM project meetings;
- gap identification;
- strategy approval;
- plan development;
- exercise preparation;
- programme maintenance; and
- continuous improvement.
The document should remain a living implementation guide. Outputs should be revised when the organisation changes, new systems are introduced, suppliers change, Critical Business Functions are redefined, incidents occur, or exercises identify weaknesses.
Training-Led BCM Implementation
This eBook is also provided as part of a value-added and complementary implementation service for organisations seeking to implement or upgrade their BCM programmes while participating in BCM Institute certification or competency-based training.
The training-led implementation approach is intended to bridge the gap between learning BCM concepts and actually applying them within the organisation.
A conventional training approach may end with participants understanding terminology and methodology.
The training-led implementation approach continues further:
Learn the Methodology
→ Understand the Organisation
→ Apply the Templates
→ Develop Organisational Outputs
→ Review with Facilitators
→ Validate with Business Owners
→ Implement Improvements
→ Exercise
→ Maintain
Participants are therefore encouraged to use the concepts covered during training to prepare actual or draft BCM project outputs for their organisation.
This provides several benefits.
First, participants can immediately contextualise the methodology rather than attempting to interpret it months after training.
Second, the organisation receives a structured set of draft outputs that can accelerate implementation.
Third, business owners can review tangible BCM requirements rather than abstract concepts.
Fourth, areas of uncertainty or disagreement become visible early and can be resolved through workshops and management review.
Finally, the approach strengthens internal capability because organisational personnel participate directly in developing the BCM programme rather than relying entirely on an external consultant.
The eBook should nevertheless not be treated as replacing management validation, professional judgement, or organisation-specific governance. Illustrative assumptions must ultimately be confirmed by MCMC.
How to Use This eBook
The most effective approach is to work through the BCM phases sequentially while allowing feedback between them.
Step 1 — Confirm the Organisational Context
Review the material established in eBooks 1 and 2.
Confirm:
- organisational scope;
- products and services;
- Critical Business Functions;
- management ownership;
- project governance; and
- BCM assumptions.
Step 2 — Complete the Risk Analysis and Review
Identify relevant threats, review controls, and determine current risk.
Step 3 — Conduct the BIA
For each CBF:
Decompose → Assess Impact → Determine RTO → Identify Systems → Map Dependencies → Identify Vital Records
Step 4 — Develop Business Continuity Strategies
Use the BIA and RAR outputs to determine:
Mitigation → Recovery Method → Recovery Location → Minimum Resources
Step 5 — Develop the Business Continuity Plans
Convert approved strategies into clear procedures for each relevant business team.
Step 6 — Exercise the Arrangements
Validate assumptions through:
- walkthroughs;
- tabletop exercises;
- simulations;
- alternate-site tests;
- remote-working tests;
- manual-workaround exercises;
- IT disaster recovery exercises; and
- supplier exercises.
Step 7 — Update the BCM Documentation
Lessons should flow back into the earlier analysis.
Exercise Finding
→ BIA Assumption Review
→ Strategy Adjustment
→ Plan Revision
→ Control Improvement
This creates the continuous improvement cycle expected of a mature BCM programme.
Moving from BCM Documentation to BCM Capability
Completing templates is necessary, but it should not become the objective of the BCM project.
The objective is organisational capability.
A completed BIA does not create resilience unless its RTOs influence recovery decisions.
A documented recovery strategy does not create resilience unless the required people, facilities, technology, and suppliers can actually be mobilised.
A Business Continuity Plan does not create resilience unless personnel understand it and can execute it.
The progression should therefore be:
Documented
→ Approved
→ Resourced
→ Implemented
→ Exercised
→ Demonstrated
→ Maintained
This distinction is particularly important in an ISO 22301-aligned BCM programme because evidence of documentation alone provides limited assurance that the organisation can actually continue its priority activities during disruption.
This third eBook marks the transition from understanding BCM and organising the BCM programme to performing the detailed analytical and planning work required for implementation.
The first two eBooks provide the foundation. This eBook turns that foundation into an implementation pathway covering:
Risk Analysis and Review
→ Business Impact Analysis
→ Business Continuity Strategy
→ Business Continuity Plan Development
Within the RAR phase, MCMC identifies credible threats, evaluates controls, and determines current risk.
Within the BIA phase, the organisation identifies its Critical Business Functions, decomposes them into Sub-Critical Business Functions, evaluates impact over time, establishes recovery requirements, and identifies supporting technology, dependencies, and vital records.
Within the BCS phase, those requirements are converted into mitigation strategies, recovery strategies, and minimum resource requirements.
Within the Plan Development phase, the approved strategies become practical procedures that personnel can use during an actual disruption.
The proposed Critical Business Functions provide the starting point for this implementation work:
CBF-1 Communications and Multimedia Regulatory Oversight
through
CBF-12 Postal and Courier Regulatory Oversight.
Each should ultimately be analysed at the Sub-CBF level rather than treated as a single indivisible activity.
The implementation logic for the remainder of the eBook is therefore:
Understand What Matters
→ Identify What Can Disrupt It
→ Determine How Quickly It Must Recover
→ Identify What It Depends Upon
→ Select How It Will Recover
→ Determine What Resources Are Required
→ Document What Personnel Must Do
→ Exercise the Arrangements
→ Improve
As a training-led implementation resource, this eBook is intended to help organisations convert the learning gained through BCM Institute's certification and competency-based training into structured organisational outputs. It provides a practical bridge between BCM education and BCM implementation, while leaving final validation, approval, and ownership with the organisation itself.
The purpose of starting BCM implementation is therefore not merely to complete a series of templates. It is to establish a credible and demonstrable capability for MCMC to continue its priority regulatory responsibilities, recover affected business functions within approved timeframes, protect stakeholders, and restore normal operations following disruption.


More Information About Business Continuity Management Courses

 To learn more about the course and schedule, click the buttons below for the BCM-300 Business Continuity Management Implementer [B-3] course and the BCM-5000 Business Continuity Management Expert Implementer [B-5].